Stay Ahead, Stay ONMINE

From COBOL to chaos: Elon Musk, DOGE, and the Evil Housekeeper Problem

In trying to make sense of the wrecking ball that is Elon Musk and President Trump’s DOGE, it may be helpful to think about the Evil Housekeeper Problem. It’s a principle of computer security roughly stating that once someone is in your hotel room with your laptop, all bets are off. Because the intruder has physical access, you are in much more trouble. And the person demanding to get into your computer may be standing right beside you. So who is going to stop the evil housekeeper from plugging a computer in and telling IT staff to connect it to the network? What happens if someone comes in and tells you that you’ll be fired unless you reveal the authenticator code from your phone, or sign off on a code change, or turn over your PIV card, the Homeland Security–approved smart card used to access facilities and systems and securely sign documents and emails? What happens if someone says your name will otherwise be published in an online list of traitors? Already the new administration is firing, putting on leave, or outright escorting from the building people who refuse to do what they’re told.  It’s incredibly hard to protect a system from someone—the evil housekeeper from DOGE—who has made their way inside and wants to wreck it. This administration is on the record as wanting to outright delete entire departments. Accelerationists are not only setting policy but implementing it by working within the administration. If you can’t delete a department, then why not just break it until it doesn’t work?  That’s why what DOGE is doing is a massive, terrifying problem, and one I talked through earlier in a thread on Bluesky.  Government is built to be stable. Collectively, we put systems and rules in place to ensure that stability. But whether they actually deliver and preserve stability in the real world isn’t actually about the technology used; it’s about the people using it. When it comes down to it, technology is a tool to be used by humans for human ends. The software used to run our democratically elected government is deployed to accomplish goals tied to policies: collecting money from people, or giving money to states so they can give money to people who qualify for food stamps, or making covid tests available to people. Usually, our experience of government technology is that it’s out of date or slow or unreliable. Certainly not as shiny as what we see in the private sector. And that technology changes very, very slowly, if it happens at all.  It’s not as if people don’t realize these systems could do with modernization. In my experience troubleshooting and modernizing government systems in California and the federal government, I worked with Head Start, Medicaid, child welfare, and logistics at the Department of Defense. Some of those systems were already undergoing modernization attempts, many of which were and continue to be late, over budget, or just plain broken. But the changes that are needed to make other systems more modern were frequently seen as too risky or too expensive. In other words, not important enough.  Of course, some changes are deemed important enough. The covid-19 pandemic and our unemployment insurance systems offer good examples. When covid hit, certain critical government technologies suddenly became visible. Those systems, like unemployment insurance portals, also became politically important, just like the launch of the Affordable Care Act website (which is why it got so much attention when it was botched).  Political attention can change everything. During the pandemic, suddenly it wasn’t just possible to modernize and upgrade government systems, or to make them simpler, clearer, and faster to use. It actually happened. Teams were parachuted in. Overly restrictive rules and procedures were reassessed and relaxed. Suddenly, government workers were allowed to work remotely and to use Slack. However, there is a reason this was an exception.  In normal times, rules and procedures are certainly part of what makes it very, very hard to change government technology. But they are in place to stop changes because, well, changes might break those systems and government doesn’t work without them working consistently.  A long time ago I worked on a mainframe system in California—the kind that uses COBOL. It was as solid as a rock and worked day in, day out. Because if it didn’t, and reimbursements weren’t received for Medicaid, then the state might become temporarily insolvent.  That’s why many of the rules about technology in government make it hard to make changes: because sometimes the risk of things breaking is just too high. Sometimes what’s at stake is simply keeping money flowing; sometimes, as with 911, lives are on the line. Still, government systems and the rules that govern them are ultimately only as good as the people who oversee and enforce them. The technology will only do (and not do) what people tell it to. So if anyone comes in and breaks those rules on purpose—without fear of consequence—there are few practical or technical guardrails to prevent it.  One system that’s meant to do that is the ATO, or the Authority to Operate. It does what it says: It lets you run a computer system. You are not supposed to operate a system without one.  But DOGE staffers are behaving in a way that suggests they don’t care about getting ATOs. And nothing is really stopping them. (Someone on Bluesky replied to me: “My first thought about the OPM [email] server was, “there’s no way those fuckers have an ATO.”)  You might think that there would be technical measures to stop someone right out of high school from coming in and changing the code to a government system. That the system could require two-factor authentication to deploy the code to the cloud. That you would need a smart card to log in to a specific system to do that. Nope—all those technical measures can be circumvented by coercion at the hands of the evil housekeeper.  Indeed, none of our systems and rules work without enforcement, and consequences flowing from that enforcement. But to an unprecedented degree, this administration, and its individual leaders, have shown absolutely no fear. That’s why, according to Wired, the former X and SpaceX engineer and DOGE staffer Marko Elez had the “ability not just to read but to write code on two of the most sensitive systems in the US government: the Payment Automation Manager and Secure Payment System at the Bureau of the Fiscal Service (BFS).” (Elez reportedly resigned yesterday after the Wall Street Journal began reporting on a series of racist comments he had allegedly made.) We’re seeing in real time that there are no practical technical measures preventing someone from taking a spanner to the technology that keeps our government stable, that keeps society running every day—despite the very real consequences.  So we should plan for the worst, even if the likelihood of the worst is low.  We need a version of the UK government’s National Risk Register, covering everything from the collapse of financial markets to “an attack on government” (but, unsurprisingly, that risk is described in terms of external threats). The register mostly predicts long-term consequences, with recovery taking months. That may end up being the case here.  We need to dust off those “in the event of an emergency” disaster response procedures dealing with the failure of federal government—at individual organizations that may soon hit cash-flow problems and huge budget deficits without federal funding, at statehouses that will need to keep social programs running, and in groups doing the hard work of archiving and preserving data and knowledge. In the end, all we have is each other—our ability to form communities and networks to support, help, and care for each other. Sometimes all it takes is for the first person to step forward, or to say no, and for us to rally around so it’s easier for the next person. In the end, it’s not about the technology—it’s about the people. Dan Hon is principal of Very Little Gravitas, where he helps turn around and modernize large and complex government services and products.
In trying to make sense of the wrecking ball that is Elon Musk and President Trump’s DOGE, it may be helpful to think about the Evil Housekeeper Problem. It’s a principle of computer security roughly stating that once someone is in your hotel room with your laptop, all bets are off. Because the intruder has physical access, you are in much more trouble. And the person demanding to get into your computer may be standing right beside you.

So who is going to stop the evil housekeeper from plugging a computer in and telling IT staff to connect it to the network?

What happens if someone comes in and tells you that you’ll be fired unless you reveal the authenticator code from your phone, or sign off on a code change, or turn over your PIV card, the Homeland Security–approved smart card used to access facilities and systems and securely sign documents and emails? What happens if someone says your name will otherwise be published in an online list of traitors? Already the new administration is firing, putting on leave, or outright escorting from the building people who refuse to do what they’re told. 

It’s incredibly hard to protect a system from someone—the evil housekeeper from DOGE—who has made their way inside and wants to wreck it. This administration is on the record as wanting to outright delete entire departments. Accelerationists are not only setting policy but implementing it by working within the administration. If you can’t delete a department, then why not just break it until it doesn’t work? 

That’s why what DOGE is doing is a massive, terrifying problem, and one I talked through earlier in a thread on Bluesky. 

Government is built to be stable. Collectively, we put systems and rules in place to ensure that stability. But whether they actually deliver and preserve stability in the real world isn’t actually about the technology used; it’s about the people using it. When it comes down to it, technology is a tool to be used by humans for human ends. The software used to run our democratically elected government is deployed to accomplish goals tied to policies: collecting money from people, or giving money to states so they can give money to people who qualify for food stamps, or making covid tests available to people.

Usually, our experience of government technology is that it’s out of date or slow or unreliable. Certainly not as shiny as what we see in the private sector. And that technology changes very, very slowly, if it happens at all. 

It’s not as if people don’t realize these systems could do with modernization. In my experience troubleshooting and modernizing government systems in California and the federal government, I worked with Head Start, Medicaid, child welfare, and logistics at the Department of Defense. Some of those systems were already undergoing modernization attempts, many of which were and continue to be late, over budget, or just plain broken. But the changes that are needed to make other systems more modern were frequently seen as too risky or too expensive. In other words, not important enough. 

Of course, some changes are deemed important enough. The covid-19 pandemic and our unemployment insurance systems offer good examples. When covid hit, certain critical government technologies suddenly became visible. Those systems, like unemployment insurance portals, also became politically important, just like the launch of the Affordable Care Act website (which is why it got so much attention when it was botched). 

Political attention can change everything. During the pandemic, suddenly it wasn’t just possible to modernize and upgrade government systems, or to make them simpler, clearer, and faster to use. It actually happened. Teams were parachuted in. Overly restrictive rules and procedures were reassessed and relaxed. Suddenly, government workers were allowed to work remotely and to use Slack.

However, there is a reason this was an exception. 

In normal times, rules and procedures are certainly part of what makes it very, very hard to change government technology. But they are in place to stop changes because, well, changes might break those systems and government doesn’t work without them working consistently. 

A long time ago I worked on a mainframe system in California—the kind that uses COBOL. It was as solid as a rock and worked day in, day out. Because if it didn’t, and reimbursements weren’t received for Medicaid, then the state might become temporarily insolvent. 

That’s why many of the rules about technology in government make it hard to make changes: because sometimes the risk of things breaking is just too high. Sometimes what’s at stake is simply keeping money flowing; sometimes, as with 911, lives are on the line.

Still, government systems and the rules that govern them are ultimately only as good as the people who oversee and enforce them. The technology will only do (and not do) what people tell it to. So if anyone comes in and breaks those rules on purpose—without fear of consequence—there are few practical or technical guardrails to prevent it. 

One system that’s meant to do that is the ATO, or the Authority to Operate. It does what it says: It lets you run a computer system. You are not supposed to operate a system without one. 

But DOGE staffers are behaving in a way that suggests they don’t care about getting ATOs. And nothing is really stopping them. (Someone on Bluesky replied to me: “My first thought about the OPM [email] server was, “there’s no way those fuckers have an ATO.”) 

You might think that there would be technical measures to stop someone right out of high school from coming in and changing the code to a government system. That the system could require two-factor authentication to deploy the code to the cloud. That you would need a smart card to log in to a specific system to do that. Nope—all those technical measures can be circumvented by coercion at the hands of the evil housekeeper. 

Indeed, none of our systems and rules work without enforcement, and consequences flowing from that enforcement. But to an unprecedented degree, this administration, and its individual leaders, have shown absolutely no fear. That’s why, according to Wired, the former X and SpaceX engineer and DOGE staffer Marko Elez had the “ability not just to read but to write code on two of the most sensitive systems in the US government: the Payment Automation Manager and Secure Payment System at the Bureau of the Fiscal Service (BFS).” (Elez reportedly resigned yesterday after the Wall Street Journal began reporting on a series of racist comments he had allegedly made.)

We’re seeing in real time that there are no practical technical measures preventing someone from taking a spanner to the technology that keeps our government stable, that keeps society running every day—despite the very real consequences. 

So we should plan for the worst, even if the likelihood of the worst is low. 

We need a version of the UK government’s National Risk Register, covering everything from the collapse of financial markets to “an attack on government” (but, unsurprisingly, that risk is described in terms of external threats). The register mostly predicts long-term consequences, with recovery taking months. That may end up being the case here. 

We need to dust off those “in the event of an emergency” disaster response procedures dealing with the failure of federal government—at individual organizations that may soon hit cash-flow problems and huge budget deficits without federal funding, at statehouses that will need to keep social programs running, and in groups doing the hard work of archiving and preserving data and knowledge.

In the end, all we have is each other—our ability to form communities and networks to support, help, and care for each other. Sometimes all it takes is for the first person to step forward, or to say no, and for us to rally around so it’s easier for the next person. In the end, it’s not about the technology—it’s about the people.

Dan Hon is principal of Very Little Gravitas, where he helps turn around and modernize large and complex government services and products.
Shape
Shape
Stay Ahead

Explore More Insights

Stay ahead with more perspectives on cutting-edge power, infrastructure, energy,  bitcoin and AI solutions. Explore these articles to uncover strategies and insights shaping the future of industries.

Shape

EmbeddingGemma 2: an open, lightweight multimodal embedding model

We introduced EmbeddingGemma last year to provide a lightweight option for high-quality text embeddings, to help your apps organize, search, and connect information directly on consumer hardware. The developer community’s response blew past our expectations. With more than 20 million downloads, builders have used it to power smarter on-device search

Read More »

Cisco readies new control plane for quantum networks

“Connecting 1,000 quantum nodes point to point takes close to 500,000 dedicated links. The switch is designed to let every node reach every other node over one shared fabric instead,” Pandey wrote.  “Once that fabric scales, deciding who gets entanglement, at what quality, in what order, with what guarantees and

Read More »

Cenovus to build oil sands business via Athabasca acquisition

“These are long-life assets located in an area where Cenovus already has a deep operating experience and strong understanding of the resource,” McKenzie said on a conference call with analysts. “They also represent one of the only remaining large-scale opportunities to add meaningful thermal reserves, resource and future development inventory within the core of the oil sands.” Among Cenovus’ growth plans is accelerating production from Athabasca’s Corner project northwest of Christina Lake by consolidating two planned expansion phases. Doing so would let Corner’s output grow to 40,000 boe/d by 2032, 3 years faster than today’s forecast. Also in the cards are efficiency projects at Athabasca’s Leismer assets that would grow production by half to about 60,000 boe/d by 2032. Michael Berger, a senior analyst at Enverus Intelligence Research, said buying Athabasca “refills Cenovus’ growth pipeline” as it relates to future production growth. The deal, he added, also “represents an escalation in oil sands deal valuations” that reflects the energy sector’s changing global dynamics. “The higher price paid by Cenovus compared to historical deals reflects a rerating of Canadian oil sands producers higher as the industry’s critical position in providing long-term oil resource in a resource-constrained world grows sharper,” Berger wrote in a commentary analyzing the acquisition plan. “While U.S. plays offer up to a decade of core inventory, the oil sands hold multiple decades. Additionally, scarcity always demands a premium and logical large-scale oil sands acquisition targets have been significantly drawn down.” The planned transaction is expected to be roughly 70% funded by cash and 30% by Cenovus shares and should close by the end of this year. It also will consolidate ownership of Duvernay Energy Corp., an oil-weighted joint venture the two companies created nearly 3 years ago that today operates more than 170 locations on roughly 90,000 net

Read More »

Energy Transfer expands Delaware basin footprint with $2.625 billion deal

@import url(‘https://fonts.googleapis.com/css2?family=Inter:wght@100..900&display=swap’); .ebm-page__main h1, .ebm-page__main h2, .ebm-page__main h3, .ebm-page__main h4, .ebm-page__main h5, .ebm-page__main h6 { font-family: Inter; } body { line-height: 150%; letter-spacing: 0.025em; } button, .ebm-button-wrapper { font-family: Inter; } .label-style { text-transform: uppercase; color: var(–color-grey); font-weight: 600; font-size: 0.75rem; } .caption-style { font-size: 0.75rem; color: color-mix(in srgb, currentColor 60%, transparent); } #onetrust-pc-sdk [id*=btn-handler], #onetrust-pc-sdk [class*=btn-handler] { background-color: #c19a06 !important; border-color: #c19a06 !important; } #onetrust-policy a, #onetrust-pc-sdk a, #ot-pc-content a { color: #c19a06 !important; } #onetrust-consent-sdk #onetrust-pc-sdk .ot-active-menu { border-color: #c19a06 !important; } #onetrust-consent-sdk #onetrust-accept-btn-handler, #onetrust-banner-sdk #onetrust-reject-all-handler, #onetrust-consent-sdk #onetrust-pc-btn-handler.cookie-setting-link { background-color: #c19a06 !important; border-color: #c19a06 !important; } #onetrust-consent-sdk .onetrust-pc-btn-handler { color: #c19a06 !important; border-color: #c19a06 !important; } Energy Transfer LP has agreed to acquire Vaquero Midstream LLC in a $2.625-billion bolt-on deal to add natural gas gathering and processing assets in the southern Delaware basin of the Texas Permian.   Vaquero holds a 300-mile pipeline network that serves operators across the basin, including in Loving, Reeves, Ward, and Winkler Counties, Tex., and operates the Caymus processing complex in Coyanosa, Pecos County, Tex., near Waha, which includes three processing trains with 675 MMcfd capacity. The company owns acreage to support construction of two additional trains that could increase total processing capacity at the site to about 1.2 bcfd. <!–> –> <!–> April 29, 2025 ]–> <!–> The Vaquero assets are interconnected with Energy Transfer’s downstream natural gas and NGL infrastructure, which Energy Transfer said could generate incremental revenue opportunities through pipeline transportation, fractionation, terminalling, and export services. Vaquero is supported by long-term, fee-based contracts with average remaining life of 10 years, and 100,000 dedicated acres. Consideration for the deal, which is expected to close in this year’s fourth quarter subject to customary conditions, consists of $1.95 billion in cash and about 33.3 million newly issued Energy Transfer common units. ]–>

Read More »

Energy Department Announces $4.2 Billion Investment to Boost Nuclear Power and Help Lower Energy Costs in Pennsylvania and Ohio

WASHINGTON—The U.S. Department of Energy’s (DOE) Office of Energy Dominance Financing (EDF) today announced a conditional loan commitment of up to $4.2 billion to finance nuclear uprates and modernization across Vistra’s nuclear fleet in Pennsylvania and Ohio. Today’s announcement will deliver more reliable American energy, strengthen the grid, lower costs, and meet growing power demand across the 13-state PJM Interconnection, L.L.C. (PJM) region. The investment advances President Trump’s Executive Order Reinvigorating the Nuclear Industrial Base, and marks another major step in restoring American nuclear leadership. “President Trump promised to unleash an American nuclear renaissance, and the Energy Department is delivering,” said U.S. Secretary of Energy Chris Wright. “By getting more power out of the nuclear plants we already have, we can deliver more affordable, reliable, around the-clock energy for American families and businesses.” The projects will preserve nearly 4 gigawatts (GW) of reliable baseload power—enough to power more than 3 million homes—and add 433 megawatts (MW) of new nuclear capacity, helping meet growing electricity demand in Pennsylvania, Ohio, and across the PJM region. The investments will support approximately 3,000 project-related jobs in engineering, construction, and planned outage work while preserving thousands of permanent, well-paying jobs. “President Trump and Secretary Wright have set a clear direction for America’s nuclear future, and EDF is financing the projects that advance that mission,” said EDF Director Gregory A. Beard. “These investments will extend the life of existing reactors, increase nuclear generation, and deliver abundant, around-the-clock power to lower costs and power American prosperity for decades to come.” Vistra’s planned investments at Beaver Valley in Pennsylvania and Davis-Besse and Perry in Ohio will produce more electricity from existing nuclear plants without requiring new transmission corridors or equivalent new generation resources, while supporting the plants’ operation for an additional 20 years beyond their existing licenses. EDF’s

Read More »

Energy Department Announces Alaska Railbelt Transmission Project to Receive Defense Production Act Funding, Securing Alaska Military Installations and Local Communities

WASHINGTON—The U.S. Department of Energy today announced its intent to deploy Defense Production Act (DPA) funding to develop a second high-voltage connection between Southcentral and Interior Alaska, strengthening grid infrastructure essential to national defense. The Alaska Energy Authority’s Beluga-Healy Transmission Project combines up to $150 million in DPA funding with $268 million in non-federal funding, representing a planned total investment of $418 million in Alaska’s grid.  Approximately 223 miles of new transmission line connecting Beluga and Healy will be built. Once complete, grid operators will have an additional pathway to move power between Alaska’s most densely populated communities and major military installations–lowering electricity costs and strengthening grid reliability for approximately 75% of Alaska’s population. Thanks to President Trump and the passage of the Working Families Tax Cut, $1 billion in federal funding has been appropriated for energy-related projects deemed critical to national security. Presidential Determination No. 2026-10 identifies transmission lines and conductors, substations, and power-control and protection equipment as essential to national defense. “Supporting improvements to Alaska’s transmission infrastructure with Defense Production Act funds reflects the Trump Administration’s commitment to strengthening national security, improving grid reliability, and lowering electricity costs,” U.S. Secretary of Energy Chris Wright said. “Thanks to Senator Sullivan, I received an extensive briefing from the Alaska Energy Authority during my recent visit to Anchorage in August. This meeting, combined with briefings from Alaska Command, confirmed the need to support an expansion of Alaska’s energy infrastructure. This project will not only support the major U.S. military expansion currently underway in Alaska, but also mining and other resource development critical to our national security.” “Alaska’s weather is unforgiving, and its grid needs another way to keep power moving,” said Office of Electricity Assistant Secretary Katie Jereza. “Beluga-Healy will provide that critical second route, helping protect communities from disruptions and

Read More »

Petrobras makes additional discovery offshore Amapá

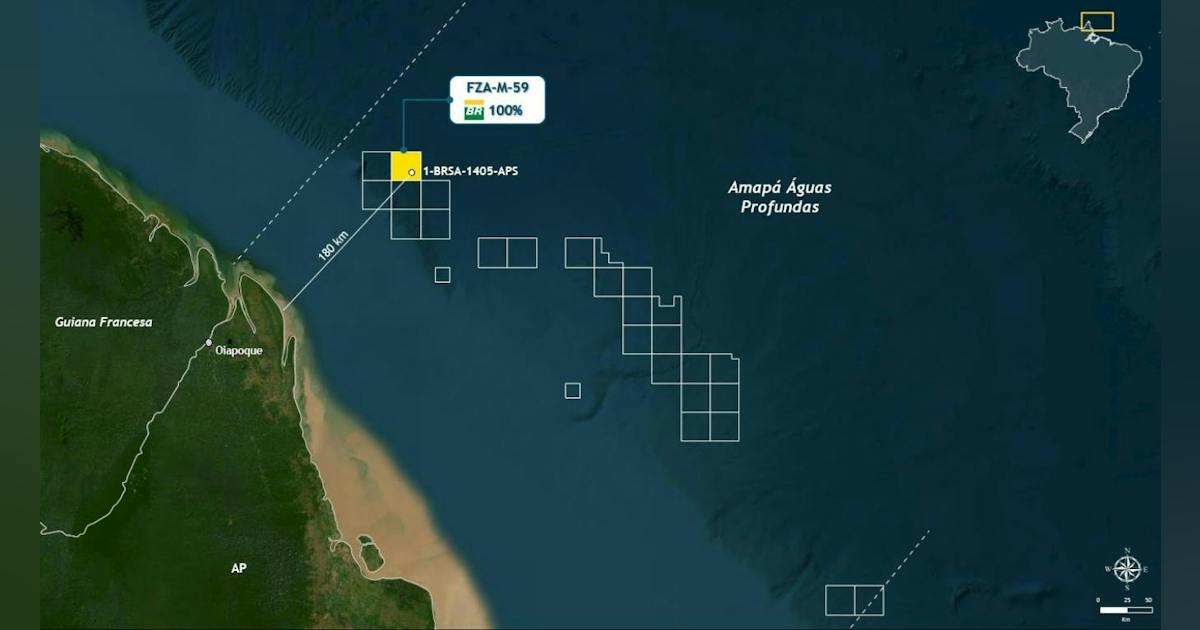
Petroleo Brasileiro SA (Petrobras) made a new discovery in block FZA-M-59 on the Brazilian Equatorial Margin, about 175 km off the coast of Amapá, in the Foz do Amazonas basin. The Morpho well (1-BRSA-1405-APS), drilled in 2,886 m of water off the coast of the state of Amapá, has reached another oil-bearing interval, the operator said on Oct. 2. Following announcement of the deepwater discovery in August, ongoing drilling of the well aimed to evaluate deeper exploratory intervals of the discovery, which was identified through electrical profiles, rock indications, and fluid samples obtained during the operations. Petrobras said the new discovery expands knowledge about the exploratory potential of the area and will provide additional information for the evaluation of the petroleum systems and resource potential of the Foz do Amazonas Sedimentary basin. With analyses still ongoing, information collected will later be characterized through laboratory analysis and integrated into the set of data acquired during drilling. Analysis already carried out, however, confirms good oil quality, according to the operator. Petrobras said it will conclude drilling activities of the well and continue the evaluation of the identified formations. Block FZA-M-59 is part of the company’s strategy to replenish oil and gas reserves through exploration in frontier areas. Petrobras is operator of the block and holds a 100% stake in the area.

Read More »

US BLM sets December California oil, gas lease sale

The US Bureau of Land Management’s (BLM) California field office Oct. 1 announced a Dec. 1 oil and gas lease sale covering 43 parcels and about 35,000 acres in California, advancing President Trump’s plan to restart federal leasing in the state after years of litigation and environmental review. While about 97% of the acreage offered lies in Kern County, BLM also plans to auction smaller, isolated parcels in Kings, Fresno, and San Luis Obispo counties. More than 95% of federal drilling operations in California currently take place in established fields in the Kern County area of the San Joaquin Valley, according to BLM. More than half of the proposed lease acreage involves a split estate, in which the federal government owns the underlying oil and gas minerals while a private party owns the surface land. The announcement opens a 30-day public protest period that will close Nov. 2. BLM completed initial scoping for the parcels in July and concluded a public comment period on the lease plan and environmental assessment in September. California Atty. Gen. Rob Bonta criticized BLM’s environmental analysis, released in August, saying the review relies on earlier planning documents and fails to adequately account for California’s restrictions on drilling near homes and schools and its phaseout of hydraulic fracturing.

Read More »

AI Is Turning Energy Storage Into Active Power Infrastructure

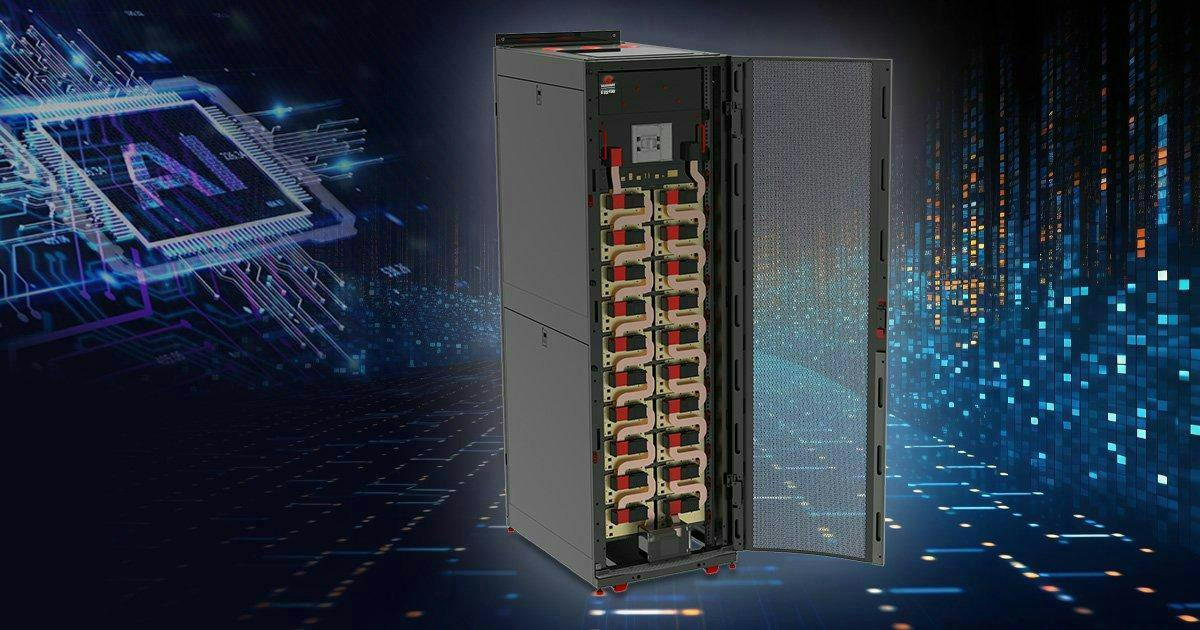
AI Turns the Power Problem Into a Transient Problem At the heart of the issue is the changing behavior of the IT load. In a conventional data center, DeLattre said, large numbers of independent loads create a relatively predictable electrical profile. AI clusters introduce much greater synchronization. As GPUs begin processing a common workload, large numbers of accelerators can increase their power consumption simultaneously. Instead of asking the electrical infrastructure to serve a relatively smooth load, the facility can experience fast power pulses moving through the system. Hybrid supercapacitors are intended to act as a buffer between that dynamic compute load and the infrastructure supplying it. During an upward transient, storage provides some of the incremental power demanded by the IT load. When demand falls, the storage system recharges. The objective is not to create additional energy. It is to keep every upstream component — from the UPS to generators and ultimately the utility connection — from having to respond directly to every rapid change taking place inside the AI cluster. From the perspective of the upstream power source, DeLattre said, the goal is to make a highly dynamic AI load appear significantly smoother. That distinction between energy and power is central to Musashi’s argument for hybrid supercapacitors. A conventional supercapacitor, also known as an electric double-layer capacitor, can deliver very high power almost instantly but stores relatively little energy. A lithium-ion battery can store considerably more energy, but DeLattre argues that it is less suited to being aggressively charged and discharged tens or hundreds of thousands of times. Musashi’s hybrid technology uses a capacitor architecture with a lithium-doped graphite electrode intended to increase energy density while preserving the fast response and high cycling capability associated with capacitors. DeLattre reduces the distinction to a simple formulation. “Batteries are very good

Read More »

AI Infrastructure’s Next Phase: Capital, Power and the Right to Build

Capital Is Becoming Infrastructure Samsung’s $1 billion commitment to Helix Digital Infrastructure offered one of the clearest examples yet of how the capital structure surrounding AI data centers is changing. Helix was formed by KKR as an AI infrastructure platform with more than $10 billion already committed by founding investors including KKR, the Kuwait Investment Authority, NVIDIA and Vistra. Samsung’s new commitment pushes that capital base still higher. But the composition of the partnership may be more significant than another billion dollars being added to the AI infrastructure ledger. Helix is intended to invest across hyperscale data centers, power generation and transmission, fiber and other connectivity infrastructure. Samsung, meanwhile, brings capabilities extending across advanced technology, construction, energy storage and cooling. This is not simply capital chasing data center returns. It increasingly resembles an attempt to assemble the data center, energy and technology supply chain inside a single investment ecosystem. That distinction is important, because one of the defining problems of the current buildout is that capital by itself does not produce capacity. Billions of dollars can be committed long before transformers arrive, transmission is constructed, generation is secured or a campus is commissioned. The increasingly valuable infrastructure platform is therefore the one capable of controlling more of those dependencies. Lambda demonstrated another side of that evolution last week with the closing of a $1.008 billion delayed-draw term loan supporting three committed customer deployments across multiple data centers. The financing received investment-grade ratings from Morningstar DBRS and Moody’s and carries a 6.78% fixed interest rate. More importantly, it is secured by both the GPU infrastructure being financed and contracted cash flows from two investment-grade customers. Capital is drawn as infrastructure reaches commissioning milestones rather than simply being handed to Lambda upfront. That begins to make AI compute look less like speculative

Read More »

Micro data center company rolls out stackable data center for edge and AI

Stack runs on Zella Sense, a monitoring, control, and automation layer built into every Zella DC cabinet. It tracks power, cooling, servers, and suspicious activity, while monitoring things like temperature, humidity, smoke, motion, water, and doors through sensors. The system runs over SNMP, Modbus, and a full API, with email alerting and local, LDAP, RADIUS, or TACACS+ authentication. That means an edge location can be remotely monitored without requiring local staff. It also comes with access control and fire protection. Zella Stack is an indoor-only offering. Zella DC sells Zella Outback as its standalone, ruggedized outdoor micro data center, and the company says an outdoor version of Stack is planned for the second half of 2027.

Read More »

Data Center Jobs: Engineering, Construction, Commissioning, Sales, Field Service and Facility Tech Jobs Available in Major Data Center Hotspots

Each month Data Center Frontier, in partnership with Pkaza, posts some of the hottest data center career opportunities in the market. Here’s a look at some of the latest data center jobs posted on the Data Center Frontier jobs board, powered by Pkaza Critical Facilities Recruiting. Looking for Data Center Candidates? Check out Pkaza’s Active Candidate / Featured Candidate Hotlist  Lead Mechanical Engineer – Data Center DesignNew York, NY/Remote This position is also available in: Denver, CO; Indianapolis, IN; Cedar Rapids, IA; Austin, TX; White Plains, NY; Dallas, TX; Richmond, VA; Ashburn, VA; Charlotte, NC; Atlanta, GA; Phoenix, AZ; Salt Lake City, UT; Kansas City, MO; Chicago, IL; Los Angeles, CA or San Jose, CA. Our client is a leading engineering design and commissioning company that is a subject matter expert in the data center space. They will provide design coordination and construction administration, consulting and management support for the data center / mission critical facilities space with the mindset to provide reliability, energy efficiency, and sustainable design expertise when providing these consulting services for enterprise, colocation and hyperscale companies. This career-growth minded opportunity offers exciting projects with leading-edge technology and innovation as well as competitive salaries and benefits. Electrical Commissioning Agent – Data Centers Austin, TX (limited travel) Non-Traveling CxA positions available in: Indianapolis, IN; Cedar Rapids, IA; Phoenix, AZ and Columbus, OH. Traveling CxA based near any major airport, otherwise traveling to: New York, NY; White Plains, NY; Dallas, TX; Richmond, VA; Montvale, NJ; Charlotte, NC; Salt Lake City, UT; Kansas City, MO; Chesterton, IN or Chicago, IL. ***Also looking for a Lead EE and ME CxA Agents and CxA PMs. *** This opportunity is with a leading EPC company of data center design / build / commissioning solutions. This company provides a complete life cycle of solutions that are custom-fit

Read More »

Startup doxx.net hands the network controls to AI

“The whole thing is run completely by AI, so behind the scenes, I mean, it’s a network with 31 locations around the world, and internally there’s a mesh network, and I can’t, as a human being, manage all of this by myself,” Lyon said. Lyon said the team modeled every site, down to the wire and the optic, in a virtual model before building. An infrastructure management system running the company’s own AI on its own hardware then ordered the installation. It orchestrated shipping and delivery through data center APIs. Human technicians performed the remote smart hands installations. The company also built tools for agents to work with users and with the network. An agent gateway gives an AI agent an identity in the doxx.net chat app. The user pastes a credential into the agent. The agent obtains its certificate and appears in the user’s chat. Users can create group chats with several agents. In one example, Lyon said one agent runs BGP while others handle other tasks.

Read More »

DCF Poll: What Must Data Centers Prove to Keep Building at AI Scale?

For years, the data center industry’s biggest constraints were largely physical, centered on power, transmission, land, water, equipment and labor. As the AI infrastructure buildout accelerates, however, another constraint is moving rapidly to the foreground. The constraint, and the concern, is whether host communities, regulators and policymakers believe the next generation of data centers is being built on terms that work for them, too. That question received a fresh exclamation point on Oct. 2, when Amazon Web Services announced it will invest more than $1 billion over five years in U.S. communities where it operates data centers, with funding aimed at areas including energy affordability, water and natural-resource protection, workforce development and education. The initiative arrives as electricity and water consumption associated with hyperscale infrastructure faces increasing scrutiny in communities across the country. And AWS is responding to a policy environment that is changing quickly. In Virginia, Loudoun County supervisors have begun a process that could pause action on certain new data center and substation applications for as long as 12 months while the county reviews its development policies. The board is scheduled to consider the proposed pause Oct. 20. Just next door, Prince William County voted Sept. 22 to dramatically shrink the area where data centers can be developed by right, largely shifting future projects outside the revised overlay into a case-by-case special-use permitting process. The issue is spreading well beyond Northern Virginia. On Sept. 23, Maryland Gov. Wes Moore signed an executive order creating a statewide framework for data center development centered on ratepayer protection, environmental impacts, community participation, transparency and accountability. Meanwhile, the U.S. House on Sept. 16 passed the Ratepayer Protection Act by a 417–3 vote, seeking to prevent data centers and other large loads from shifting the incremental costs of new generation and grid infrastructure onto

Read More »

Microsoft will invest $80B in AI data centers in fiscal 2025

And Microsoft isn’t the only one that is ramping up its investments into AI-enabled data centers. Rival cloud service providers are all investing in either upgrading or opening new data centers to capture a larger chunk of business from developers and users of large language models (LLMs).  In a report published in October 2024, Bloomberg Intelligence estimated that demand for generative AI would push Microsoft, AWS, Google, Oracle, Meta, and Apple would between them devote $200 billion to capex in 2025, up from $110 billion in 2023. Microsoft is one of the biggest spenders, followed closely by Google and AWS, Bloomberg Intelligence said. Its estimate of Microsoft’s capital spending on AI, at $62.4 billion for calendar 2025, is lower than Smith’s claim that the company will invest $80 billion in the fiscal year to June 30, 2025. Both figures, though, are way higher than Microsoft’s 2020 capital expenditure of “just” $17.6 billion. The majority of the increased spending is tied to cloud services and the expansion of AI infrastructure needed to provide compute capacity for OpenAI workloads. Separately, last October Amazon CEO Andy Jassy said his company planned total capex spend of $75 billion in 2024 and even more in 2025, with much of it going to AWS, its cloud computing division.

Read More »

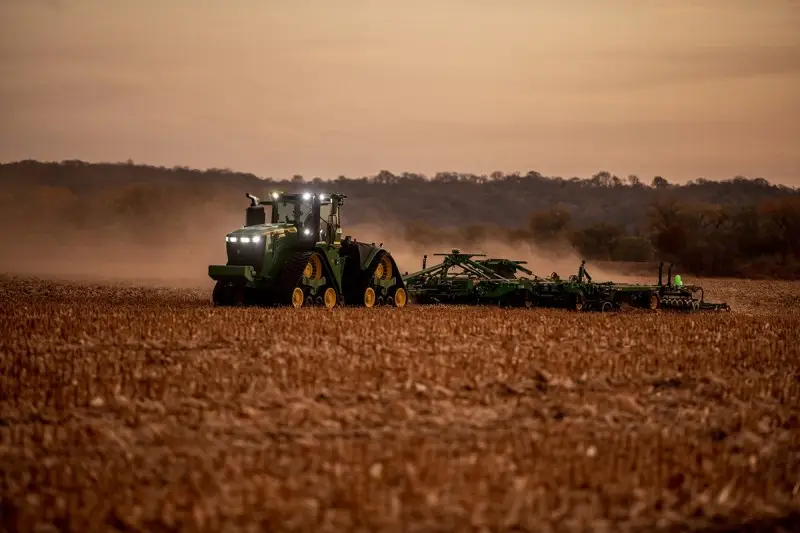
John Deere unveils more autonomous farm machines to address skill labor shortage

Join our daily and weekly newsletters for the latest updates and exclusive content on industry-leading AI coverage. Learn More Self-driving tractors might be the path to self-driving cars. John Deere has revealed a new line of autonomous machines and tech across agriculture, construction and commercial landscaping. The Moline, Illinois-based John Deere has been in business for 187 years, yet it’s been a regular as a non-tech company showing off technology at the big tech trade show in Las Vegas and is back at CES 2025 with more autonomous tractors and other vehicles. This is not something we usually cover, but John Deere has a lot of data that is interesting in the big picture of tech. The message from the company is that there aren’t enough skilled farm laborers to do the work that its customers need. It’s been a challenge for most of the last two decades, said Jahmy Hindman, CTO at John Deere, in a briefing. Much of the tech will come this fall and after that. He noted that the average farmer in the U.S. is over 58 and works 12 to 18 hours a day to grow food for us. And he said the American Farm Bureau Federation estimates there are roughly 2.4 million farm jobs that need to be filled annually; and the agricultural work force continues to shrink. (This is my hint to the anti-immigration crowd). John Deere’s autonomous 9RX Tractor. Farmers can oversee it using an app. While each of these industries experiences their own set of challenges, a commonality across all is skilled labor availability. In construction, about 80% percent of contractors struggle to find skilled labor. And in commercial landscaping, 86% of landscaping business owners can’t find labor to fill open positions, he said. “They have to figure out how to do

Read More »

2025 playbook for enterprise AI success, from agents to evals

Join our daily and weekly newsletters for the latest updates and exclusive content on industry-leading AI coverage. Learn More 2025 is poised to be a pivotal year for enterprise AI. The past year has seen rapid innovation, and this year will see the same. This has made it more critical than ever to revisit your AI strategy to stay competitive and create value for your customers. From scaling AI agents to optimizing costs, here are the five critical areas enterprises should prioritize for their AI strategy this year. 1. Agents: the next generation of automation AI agents are no longer theoretical. In 2025, they’re indispensable tools for enterprises looking to streamline operations and enhance customer interactions. Unlike traditional software, agents powered by large language models (LLMs) can make nuanced decisions, navigate complex multi-step tasks, and integrate seamlessly with tools and APIs. At the start of 2024, agents were not ready for prime time, making frustrating mistakes like hallucinating URLs. They started getting better as frontier large language models themselves improved. “Let me put it this way,” said Sam Witteveen, cofounder of Red Dragon, a company that develops agents for companies, and that recently reviewed the 48 agents it built last year. “Interestingly, the ones that we built at the start of the year, a lot of those worked way better at the end of the year just because the models got better.” Witteveen shared this in the video podcast we filmed to discuss these five big trends in detail. Models are getting better and hallucinating less, and they’re also being trained to do agentic tasks. Another feature that the model providers are researching is a way to use the LLM as a judge, and as models get cheaper (something we’ll cover below), companies can use three or more models to

Read More »

OpenAI’s red teaming innovations define new essentials for security leaders in the AI era

Join our daily and weekly newsletters for the latest updates and exclusive content on industry-leading AI coverage. Learn More OpenAI has taken a more aggressive approach to red teaming than its AI competitors, demonstrating its security teams’ advanced capabilities in two areas: multi-step reinforcement and external red teaming. OpenAI recently released two papers that set a new competitive standard for improving the quality, reliability and safety of AI models in these two techniques and more. The first paper, “OpenAI’s Approach to External Red Teaming for AI Models and Systems,” reports that specialized teams outside the company have proven effective in uncovering vulnerabilities that might otherwise have made it into a released model because in-house testing techniques may have missed them. In the second paper, “Diverse and Effective Red Teaming with Auto-Generated Rewards and Multi-Step Reinforcement Learning,” OpenAI introduces an automated framework that relies on iterative reinforcement learning to generate a broad spectrum of novel, wide-ranging attacks. Going all-in on red teaming pays practical, competitive dividends It’s encouraging to see competitive intensity in red teaming growing among AI companies. When Anthropic released its AI red team guidelines in June of last year, it joined AI providers including Google, Microsoft, Nvidia, OpenAI, and even the U.S.’s National Institute of Standards and Technology (NIST), which all had released red teaming frameworks. Investing heavily in red teaming yields tangible benefits for security leaders in any organization. OpenAI’s paper on external red teaming provides a detailed analysis of how the company strives to create specialized external teams that include cybersecurity and subject matter experts. The goal is to see if knowledgeable external teams can defeat models’ security perimeters and find gaps in their security, biases and controls that prompt-based testing couldn’t find. What makes OpenAI’s recent papers noteworthy is how well they define using human-in-the-middle

Read More »