Network intelligence becomes the centerpiece
The most important .conf announcement for network engineers is the new Network Intelligence App for Splunk Observability. The application will bring Cisco network topology, device health, and event data into Splunk, enabling engineers to trace an alert to the affected device and understand the surrounding network context without leaving the platform. This integrated view can save hours by eliminating the dashboard switching and manual correlation that plague engineers today.
In the pre-briefing, Kamal Hathi, senior vice president and general manager for Splunk, described the operational problem in terms network engineers know all too well: When a web page runs slowly, “it’s always the network.” But the root cause could instead be an ISP, DNS provider, cloud service, or application. Network teams often see only interfaces, connections, and device state, while other groups work from their own disconnected toolsets, but network operations generally have to find the source of the problem.
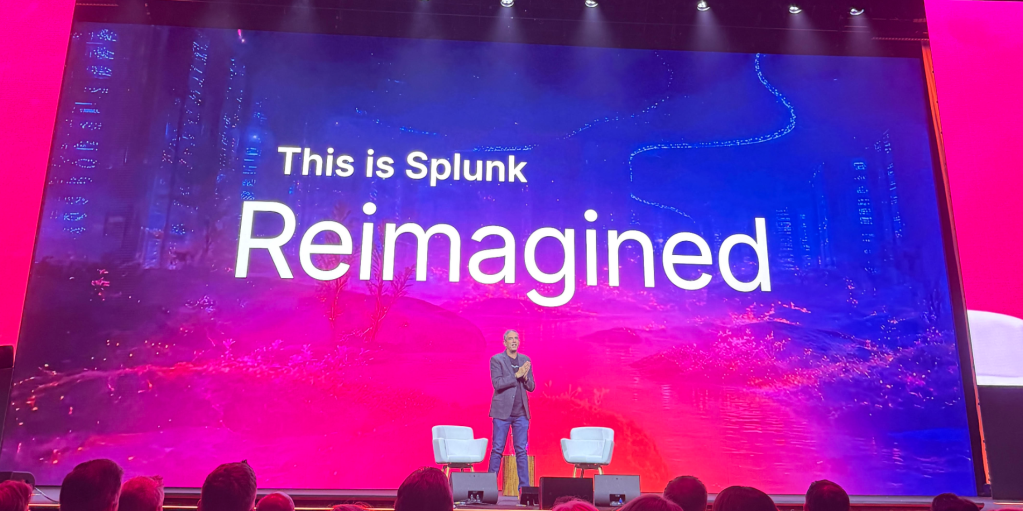
Cisco’s response is to bring the network’s topology and health signals into a shared observability plane. “The fact is, all of this runs on a common set of data that can provide end-to-end visibility across network and application domains,” said Hathi (pictured at top). That does not eliminate the need for network-specific management platforms, packet-level troubleshooting, or deep domain expertise. It can, however, change the opening moments of an incident. Rather than starting with a cross-functional argument over ownership, an operations team could begin with correlated evidence: service degradation, the affected user path, the relevant network devices, the underlying events, and the wider topology.