As such, security is becoming more demanding. For example, segmenting and securing the network around the mainframe is something mainframe shops need to pay more attention to, Dickens said. “There was a time when businesses could do a security penetration test on a network tied to the mainframe maybe once every 12 months, but that certainly isn’t very strategic now,” Dickens said. Patching, too, is become an activity that needs to be kept up with more frequently, he said.
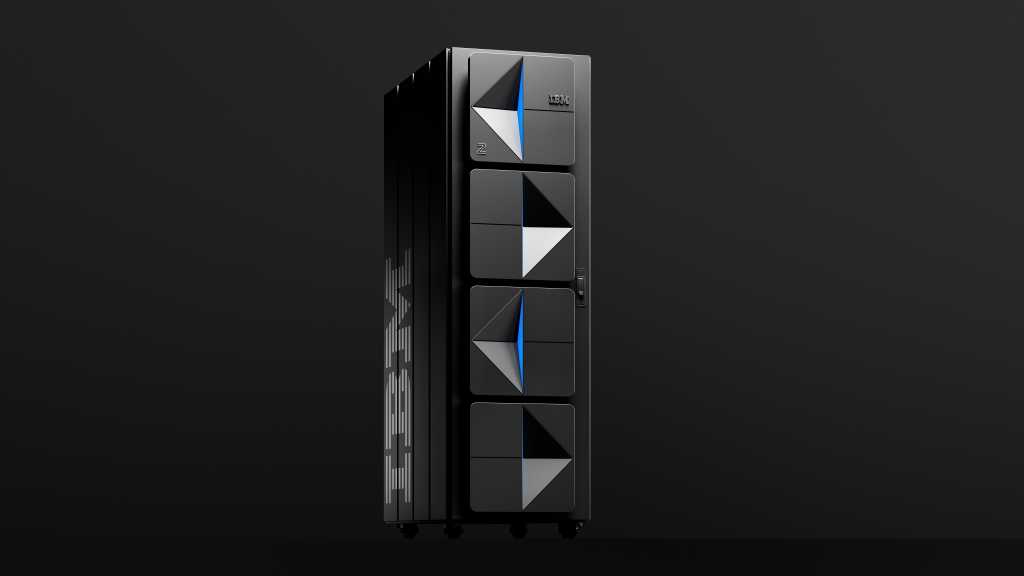
IBM this summer rolled out the zSecure Detection package that combines threat monitoring, network insights, AI-driven access anomaly detection and automated response for z/OS. It includes automated network micro-segmentation capabilities that generate customized segmentation policies based on observed networking behavior. These policies can help organizations reduce unnecessary connectivity, limit opportunities for lateral movement, and strengthen security controls across critical environments, IBM stated.
AI and the mainframe
As AI infiltrates more technology environments, IBM sees a continuing role for the mainframe. “Enterprise AI will rarely operate on one platform alone. Models, applications, and data will be distributed across mainframes, cloud platforms, accelerators and other infrastructure,” Crimmins said.