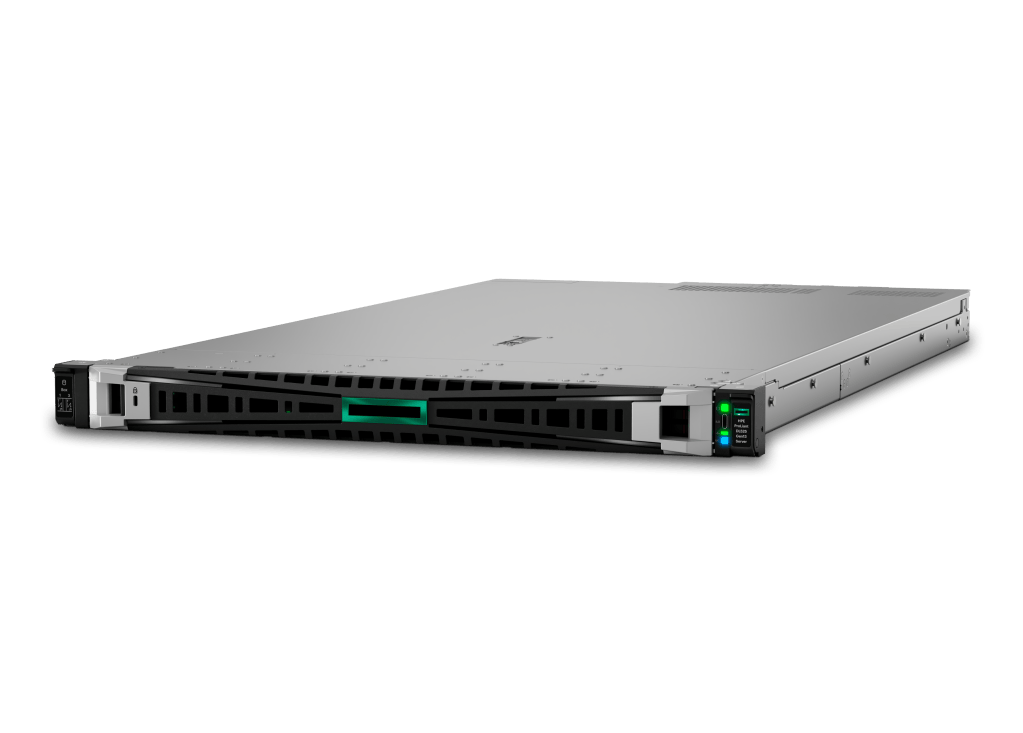
One important attribute is that HPE iLO 8 delivers auto-SED (Self-Encrypting Drive) server capabilities, automatically protecting data at rest from the moment the server is first powered on, according to Aaron Lamond, product marketing manager, HPE Compute. “No external key manager, additional configuration, or manual activation is required. Encryption stops being a setting someone has to remember and becomes a property of the server,” Lamond stated.
HPE iLO 8 also brings multi-party authorization (MPA), which requires two authorized users to approve high-impact actions, including key provisioning and secure erase, reducing the risk of single-user error or misuse, Lamond stated. In addition, iLO 8 supports expanded post-quantum cryptography (PQC), which extends beyond firmware to help protect server communication paths from emerging threats, Lamond said.
Enterprise-grade component verification, using HPE’s Silicon Root of Trust, validates the authenticity and integrity of critical server components as they are added, replaced, or modified throughout the server lifecycle, according to HPE.